
Google’s Threat Intelligence Group (GTIG) has uncovered that North Korean threat actor UNC5342 is weaponizing EtherHiding, a novel malware delivery technique leveraging public blockchains, to conduct large‑scale cryptocurrency theft.
This marks the first known instance of a nation‑state actor adopting the EtherHiding technique, previously linked to financially motivated groups like UNC5142.
Exploiting the Blockchain for Persistence
EtherHiding first emerged in 2023 as part of the CLEARFAKE campaign. It involves embedding malicious JavaScript payloads directly into blockchain smart contracts, particularly on the BNB Smart Chain and Ethereum networks, transforming decentralized ledgers into resilient, takedown‑proof command‑and‑control servers.
In UNC5342’s operations, the hackers use social engineering under the campaign name “Contagious Interview,” which impersonates recruiting processes at crypto and tech firms.
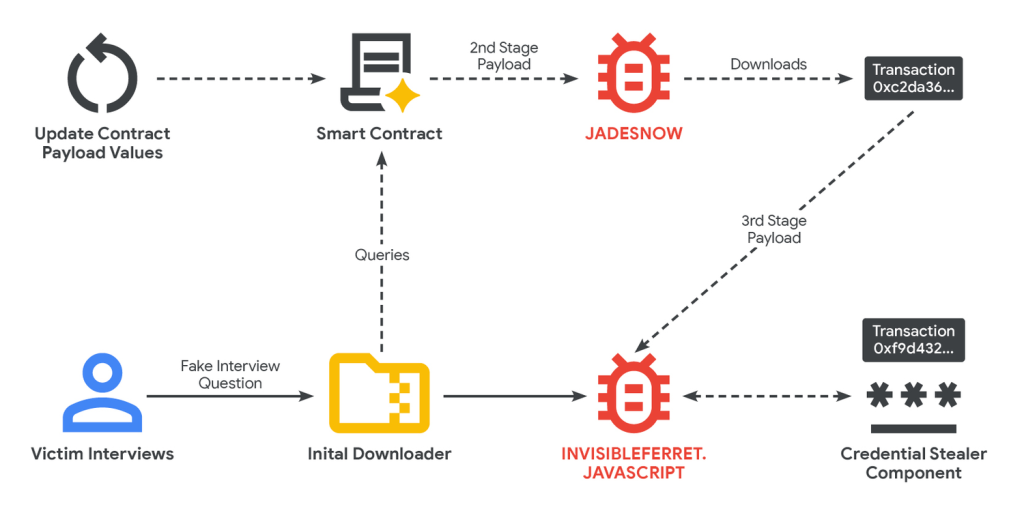
Victims are lured with fake job interviews or coding tests that deliver the JADESNOW downloader malware, which then uses EtherHiding to fetch and execute the next‑stage payload INVISIBLEFERRET.
GTIG’s analysis shows the loader retrieves malicious data from blockchain transactions via read‑only eth_call The request is for a stealthy mechanism that avoids gas fees and leaves no traceable transaction record.
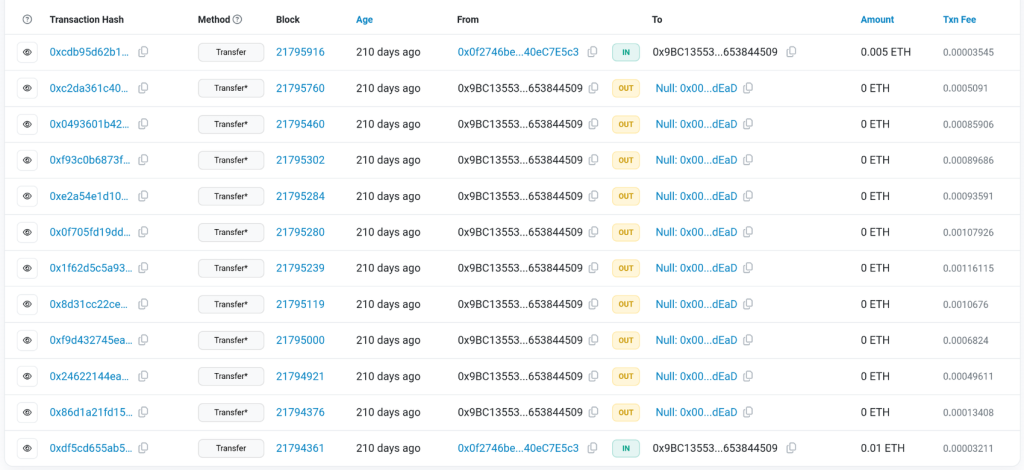
The actors frequently update their malicious smart contracts, each revision costing less than $2 in gas fees, enabling rapid reconfiguration of payload delivery.
Multi‑Stage Attack Chain and On‑Chain Operations
The infection chain begins when victims download malicious JavaScript or npm packages during the fake technical assessment phase. JADESNOW, written in JavaScript, communicates with smart contracts such as 0x8eac3198dd72f3e07108c4c7cff43108ad48a71c on the BNB Smart Chain.
The contract’s encoded and XOR‑encrypted payload spawns the next stage, INVISIBLEFERRET, which is deployed in memory to establish a remote backdoor.
Telemetry reveals INVISIBLEFERRET connects to attacker‑controlled MySQL servers on port 3306, exfiltrating system data and storing stolen credentials, session cookies, and wallet information in ZIP archives uploaded to remote servers and private Telegram chats.
UNC5342’s use of multiple blockchain networks demonstrates sophisticated operational compartmentalization, switching payload hosting between BNB Smart Chain and Ethereum for cost and evasion advantages.
GTIG emphasizes that both UNC5342 and UNC5142 rely on centralized API services, such as Binplorer or Ethplorer, rather than direct blockchain node interaction.
This dependency introduces limited mitigation opportunities for security teams to identify and block malicious API traffic, even though the blockchain data itself remains immutable.
The campaign underscores a growing trend of state‑sponsored actors abusing decentralized infrastructure to achieve persistence, anonymity, and control.
According to GTIG, EtherHiding represents a new frontier in “bulletproof” malware hosting, solidifying the convergence of Web3 technologies and nation‑state cybercrime.
Find this Story Interesting! Follow us on Google News , LinkedIn and X to Get More Instant Updates

 has uncovered that North Korean threat actor UNC5342.)