
A cybercriminal has allegedly put a 63.4MB database containing sensitive employee information from Belgian business software company Odoo up for sale on a dark web forum, claiming the data was obtained through collaboration with a senior company insider.
The unverified breach, if authentic, could expose personal and professional information of employees from one of Europe’s leading open-source business application providers.
The seller is demanding $25,000 in cryptocurrency, specifically Monero (XMR) or Bitcoin (BTC), for the complete database.
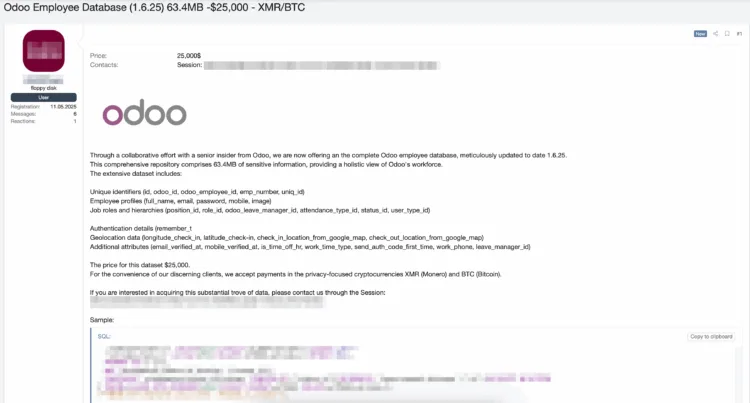
According to the dark web advertisement, the cybercriminal claims to have obtained the data through a “collaborative effort with a senior insider” from within Odoo, suggesting potential involvement of an internal threat actor.
The advertised database allegedly contains a comprehensive array of sensitive employee information. The listed data points include unique identifiers such as employee IDs, Odoo-specific identifiers, and employee numbers.
More concerning are the personal details reportedly included: full names, email addresses, passwords, mobile phone numbers, and employee photographs.
The database also allegedly contains detailed job-related information including position IDs, role classifications, leave manager assignments, and attendance type identifiers.
Perhaps most troubling are the authentication details and geolocation data supposedly included in the breach.
The seller claims the database contains authentication tokens, location coordinates for check-ins and check-outs, and Google Maps location data tied to employee movements.
Additional sensitive attributes allegedly include email and mobile verification statuses, work phone numbers, and various employee status indicators.
Odoo’s Profile
The authenticity of both the database and the seller’s claims remains unverified at this time. However, the detailed and technically specific nature of the data categories listed in the advertisement raises legitimate concerns about the potential legitimacy of the breach.
The company provides an integrated suite of open-source business applications covering customer relationship management (CRM), e-commerce platforms, accounting systems, inventory management, project coordination, and human resources software.
Their comprehensive business solution attracts millions of users worldwide, spanning from small startups to large enterprise organizations.
The company’s widespread adoption across diverse business sectors makes employee data particularly valuable to cybercriminals.
Odoo’s extensive client base and the trusted nature of their business applications mean that employee information could potentially be leveraged for various malicious purposes, including social engineering attacks, identity theft, or corporate espionage targeting the company’s clients and partners.
Security Implications
According to Report, Odoo, headquartered in Belgium, represents a significant player in the global business software market.
The comprehensive scope of allegedly compromised information suggests that if genuine, this represents a significant security incident affecting employee privacy and organizational security.
The involvement of an alleged insider threat compounds the severity of the situation, as internal actors typically have privileged access to sensitive systems and data repositories.
Such breaches are particularly challenging to prevent and detect, as they often bypass traditional external security measures.
Organizations and cybersecurity professionals are monitoring the situation closely, though official verification from Odoo or relevant authorities has not yet been announced.
The incident underscores the ongoing challenges companies face in protecting employee data from both external threats and potential insider risks in an increasingly complex cybersecurity landscape.
Find this Story Interesting! Follow us on LinkedIn and X to Get More Instant Update

.webp?fit=1068,580&ssl=1&description=A cybercriminal has allegedly put a 63.4MB database containing sensitive employee information from Belgian business software company Odoo.)