
A recent wave of cyberattacks has unveiled sophisticated distribution methods for the Rhadamanthys infostealer, leveraging seemingly benign user interaction layers such as the ClickFix Captcha to deliver advanced malware.
Security researchers identified a suspicious campaign centering around the domain hxxps://ypp-studio[.]com, where meticulously crafted PowerShell commands are employed to covertly download and execute malicious payloads.

Upon close technical analysis, the campaign demonstrates a high degree of automation and stealth, beginning with a PowerShell invocation using parameters to hide execution, bypass policy restrictions, and evade initial endpoint defenses.
Stealthy New Delivery Tactics Uncovered
The initial script sets a remote URL variable and uses .NET’s WebClient class to download and run malicious code from hxxps://ypp-studio[.]com/update.txt, launching the content in memory via Invoke-Expression (iex).
This fileless approach not only allows for immediate payload execution but also complicates forensic recovery.
Further investigation reveals that the downloaded script contains both obfuscation techniques and a hex-encoded string, which, once decoded, downloads an MSI installer masquerading as a legitimate update.
The installer, retrieved from http://62.60.226.74/PTRFHDGS.msi, is saved to the user’s AppData directory and is silently executed with msiexec.exe.
In a bid to deceive, the malware then presents a fraudulent “Verification complete!” prompt to the victim.
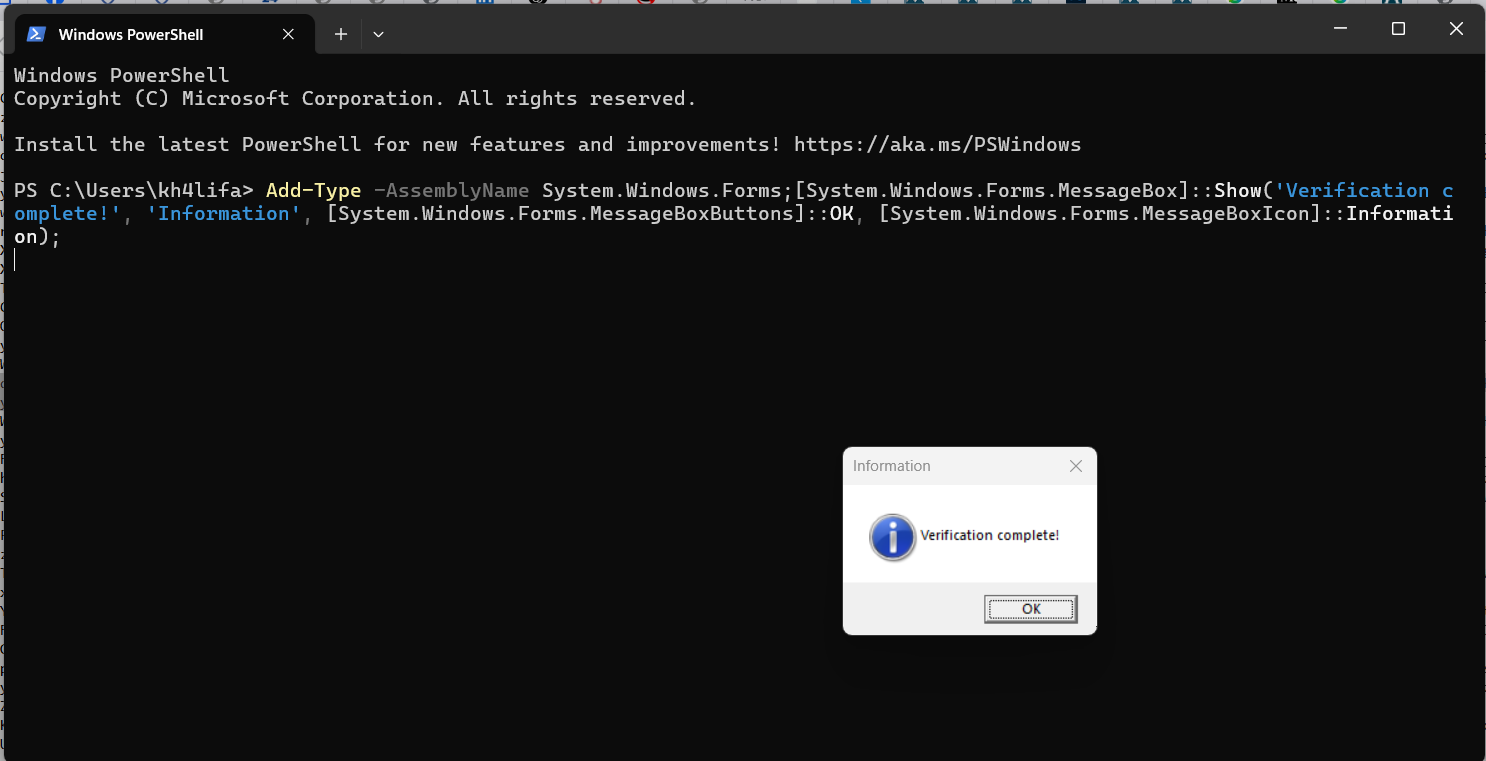
It was also observed that navigating to hxxp://62.60.226.74/PTRFHDGS[.]msi triggers an instant download of “rh_0.9.0.exe,” which has previously been associated with Rhadamanthys campaigns.
Technical Evolution
Rhadamanthys, first identified in 2022 and sold as Malware-as-a-Service (MaaS), has demonstrated continuous improvements in both its functionality and anti-analysis techniques.
Unlike earlier versions, the latest iterations rely on multi-layered evasion strategies, deploying anti-virtualization, anti-debugging, and anti-sandboxing checks.
The malware inspects running processes for a blacklist of forensic and debugging tools such as Wireshark, OllyDbg, ProcessHacker, and IDA and incorporates breakpoint detection and timing-based side-channel analysis to identify analysis environments.
When suspicious conditions are detected, the infostealer either sleeps, exits, or modifies its execution flow, further hindering traditional detection and analysis.
Network communication with the command-and-control infrastructure is handled directly via IPv4 sockets using hardcoded IPs, notably 193.109.85.136, side-stepping DNS-based detection mechanisms.
Upon infection, Rhadamanthys performs targeted data theft: it collects system information, takes screenshots, and aggressively harvests data from browsers, cryptocurrency wallets, password managers, email and FTP clients, 2FA tools, VPNs, and messaging platforms such as Telegram and Discord.
One notable development in this campaign is its reliance on social engineering and user trust manipulation.
The abuse of ClickFix Captcha serves as an entry barrier, imparting a sense of legitimacy to the victim and helping evade automated threat detection systems.
The campaign’s ability to deliver fileless payloads, coupled with frequent updates to the dropper and exfiltration modules, highlights the ongoing arms race between threat actors and defenders.
Detection remains challenging, but advanced behavioral analytics, network monitoring, and tailored Sigma rules such as those targeting suspicious PowerShell usage and registry access have proven effective in identifying the malware’s signature activities.
As Rhadamanthys continues to evolve, organizations are urged to increase employee vigilance, enforce strict web filtering, and monitor for indicators such as unusual PowerShell activity and stealthy outbound traffic.
The technical sophistication of the Rhadamanthys infostealer underscores the urgent need for layered defense strategies in the modern enterprise threat landscape.
Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant updates

