
Cybersecurity researchers have identified a new spear-phishing campaign delivering the VIP Keylogger malware, marking a shift from earlier distribution techniques by employing an AutoIt-based injector to bypass traditional defenses and deliver its malicious payload.
Notorious for its sophistication, the VIP Keylogger is designed to exfiltrate sensitive information, focusing primarily on stealing credentials and browser data from compromised systems.
From Steganography to AutoIt Injection
This campaign commences with targeted spear-phishing emails masquerading as urgently titled financial documents.

The malicious emails carry a ZIP archive named “payment receipt_USD 86,780.00 pdf.pdf.z,” which, upon extraction, reveals an executable deceptively labeled “payment receipt_USD 86,780.00 pdf.exe.”
Unsuspecting recipients are tricked into launching what appears to be a harmless PDF, initiating the infection chain.
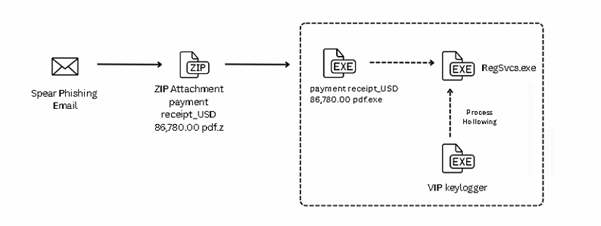
Once executed, the binary runs an embedded AutoIt script which orchestrates the execution of the final VIP Keylogger payload.
The attackers have adopted AutoIt for its obfuscation potential and capability to compile benign-looking executables, allowing them to evade many traditional security solutions.
Within the system’s TEMP directory, the malware drops two encrypted files, “leucorynx” and “aveness,” as part of its multi-stage deployment process.
The AutoIt script first decrypts “leucorynx” using a custom XOR algorithm, loading the resulting data into memory.
Leveraging DllCall routines, the script allocates executable memory and injects the decrypted payload directly into the address space of a suspended RegSvcs.exe process, a technique known as process hollowing.
This method replaces the legitimate code with the malicious VIP Keylogger, which then executes stealthily under the guise of a trusted system process.
Data Exfiltration Techniques
To maintain persistence on infected devices, the malware creates a VBS script within the Startup folder. This script ensures continued execution of the main payload, saved as “definitiveness.exe” in the user’s “AppData\Local\Dunlop” directory, after each system reboot.
The AutoIt script subsequently decrypts the secondary file “aveness,” unpacking it in memory to complete the deployment of the keylogger component.
Once established, the .NET-based VIP Keylogger aggressively targets browser-stored credentials, clipboard contents, and logged keystrokes.
Data is exfiltrated via multiple channels, including direct SMTP email communication and dedicated C2 infrastructure, maximizing the attackers’ chances of successful data theft.
Memory forensics reveal clear evidence of the process hollowing operation, with strings indicative of the keylogger’s activity present within the manipulated RegSvcs.exe process.
Analysis confirms the final payload’s dynamic decryption and in-memory execution, reducing forensic artifacts on disk and hampering detection by endpoint security solutions.
This campaign underscores the growing trend of leveraging fileless malware techniques and scripting platforms like AutoIt to evade signature-based defenses, with a renewed focus on social engineering as the initial infection vector.
Security teams are urged to enact heightened vigilance for suspicious attachments and to update defensive countermeasures against AutoIt-compiled droppers.
Indicators of Compromise (IOCs)
| Type | Value | Description |
|---|---|---|
| MD5 | F0AD3189FE9076DDD632D304E6BEE9E8 | payment receipt_USD 86,780.00 pdf.exe |
| MD5 | 0B0AE173FABFCE0C5FBA521D71895726 | VIP Keylogger |
| Domain/IP | hxxp[:]//51.38.247.67:8081 | Command and Control Server |
Find this Story Interesting! Follow us on LinkedIn and X to Get More Instant Updates

