


A new report from Silent Push Threat Analysts has revealed that numerous Western companies, including tech giants like Amazon, Microsoft, and Meta, may still be hosting accounts linked to Lizhi Liu, the administrator of the FUNNULL content delivery network (CDN).
Liu and FUNNULL were added to the U.S. Treasury’s sanctions list in May 2025 for their role in supporting fraudulent investment websites targeting Americans, prompting urgent calls for companies to terminate these accounts to comply with federal regulations.
FUNNULL’s Role in Cybercrime
The report, titled “Unveiling Triad Nexus: How FUNNULL CDN Facilitates Widespread Cyber Threats,” details how FUNNULL has become a primary hub for hosting scam websites responsible for over $200 million in losses to U.S. victims, with an average loss of $150,000 per individual.
The U.S. Treasury Department and FBI issued joint advisories in May 2025, linking FUNNULL to a majority of virtual currency investment scams reported to the FBI.
These “pig butchering” schemes exploit victims through fraudulent investment platforms hosted on FUNNULL’s infrastructure, often leveraging cryptocurrencies to obscure transactions.
Infrastructure Laundering Exposed


Silent Push has been tracking FUNNULL since 2022, uncovering its use of “Infrastructure Laundering,” a technique that hides malicious websites within legitimate Western cloud providers like Amazon and Microsoft.
This method allows threat actors to host scam sites at little to no cost, complicating efforts by cybersecurity defenders to block them.
The report labels this network of cybercriminals the “Triad Nexus,” suggesting Liu may not be the mastermind behind the scams but a key enabler through his technical expertise in managing the CDN.
Lizhi Liu’s Online Footprint
Lizhi Liu, a 41-year-old web developer from China, also known as Steve or Steven Liu, maintains active accounts on several major Western platforms, including X/Twitter, GitHub, LinkedIn, Facebook, PayPal, and WordPress.

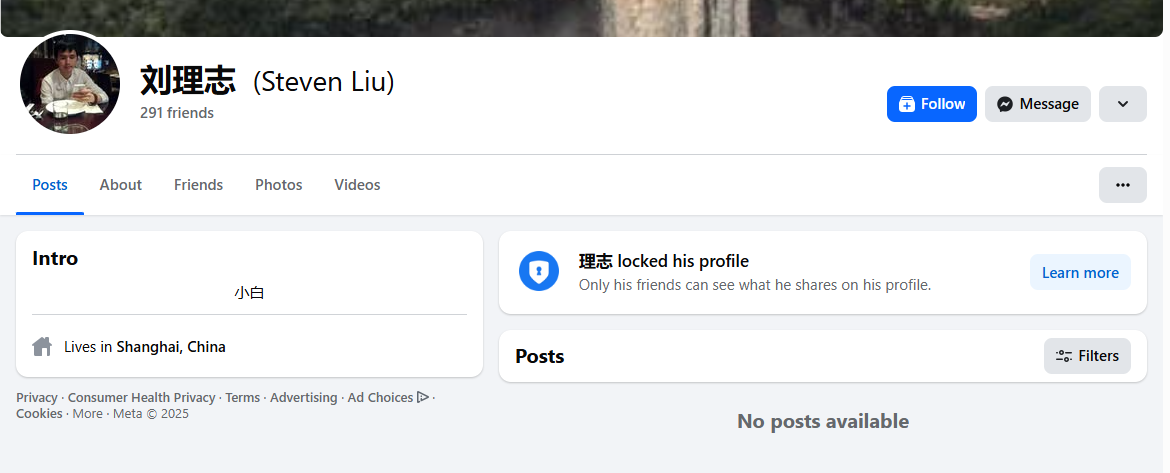
Despite the sanctions, Liu continues to engage with these platforms, notably updating a Facebook group about Ganzhou, China, as recently as June 2025.
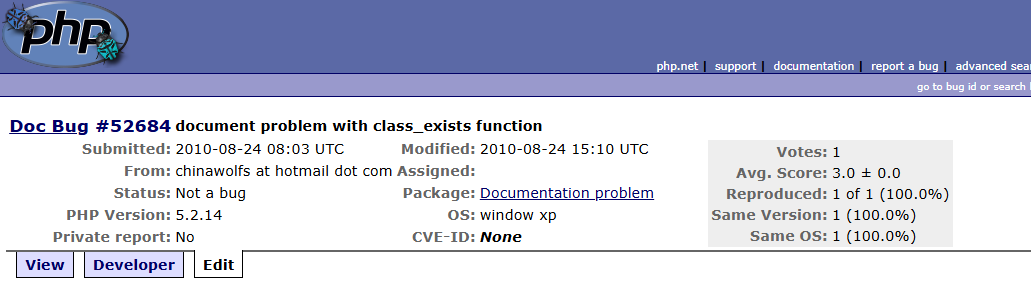
Silent Push’s investigation revealed Liu’s extensive online presence, including blogs and social media profiles dating back to 2010, where he has occasionally shared anti-American and anti-Japanese sentiments, though such political commentary is rare.

Mixed Responses from Tech Giants
The report highlights Google as one of the few companies to take decisive action, having recently terminated Liu’s YouTube channel (@nicelizhi).
However, other platforms, including Microsoft’s GitHub and Meta’s Facebook, have yet to ban Liu’s accounts, raising concerns about compliance with U.S. sanctions.
Cybersecurity expert Brian Krebs, in collaboration with Silent Push, noted in his piece, “Big Tech’s Mixed Response to U.S. Treasury Sanctions,” that companies are responding inconsistently, with some taking minimal or no action against Liu’s accounts.
Liu’s profiles reveal a complex persona: a skilled developer with a passion for open-source software, fashion, and photography.
His GitHub repositories, including one for “GunDNS,” a potential precursor to FUNNULL’s infrastructure, show significant collaboration with the developer community.


Liu’s blogs, such as models.net.cn and cnphp.wordpress.com, blend technical content with personal interests, including fashion and occasional political commentary.
His Facebook pages, promoting Ganzhou tourism and modeling, remain active, with posts as recent as August 2024.
Cryptocurrency and Money Laundering Links
The Treasury’s sanctions also tie FUNNULL to illicit cryptocurrency transactions, with blockchain analysis from Chainalysis confirming direct links to Huione Pay, a marketplace flagged by FinCEN for money laundering.
This connection underscores the broader implications of FUNNULL’s operations, which extend beyond scams to potentially destabilizing financial networks.
FinCEN has proposed classifying Huione Pay as a “financial institution of primary money laundering concern.”
Silent Push’s findings emphasize the need for Western companies to act swiftly to identify and terminate Liu’s accounts to avoid violating sanctions.
The report lists specific platforms hosting Liu’s profiles, including Medium, Hugging Face, DeviantArt, and Flickr, where over 1,000 of his photos remain publicly accessible.

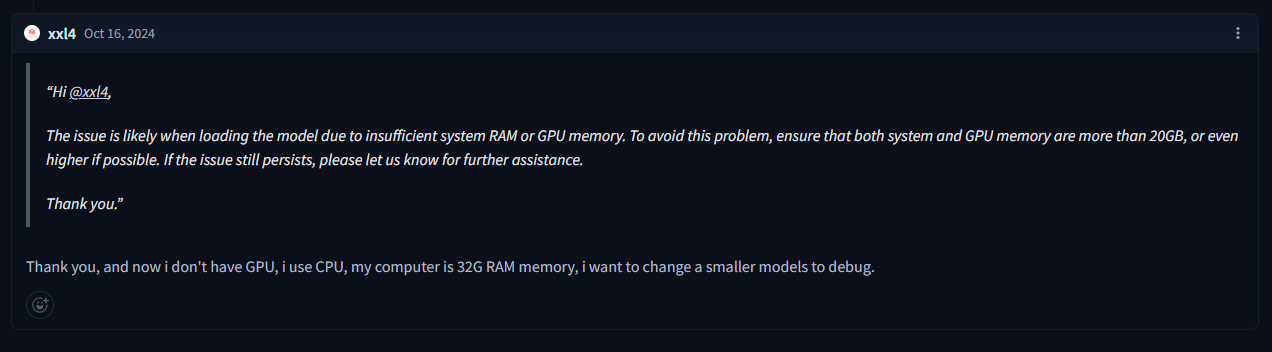
Liu’s long-standing email, chinawolfs@hotmail.com, and associated passwords have been linked to multiple breaches, further complicating efforts to track his activities.
As the FBI continues to support victims of FUNNULL-hosted scams, Silent Push urges organizations to leverage tools like its Community Edition to monitor and block related threats.
The firm’s ongoing investigation into the Triad Nexus aims to disrupt the network’s ability to exploit Western infrastructure.
For now, the responsibility falls on companies to ensure compliance with U.S. sanctions, protecting both their users and the integrity of the global financial system.
Find this Story Interesting! Follow us on Google News, LinkedIn, and X to Get More Instant updates


